
SPHEREboard Governance & Remediation
From knowing what’s there to fixing what’s wrong.
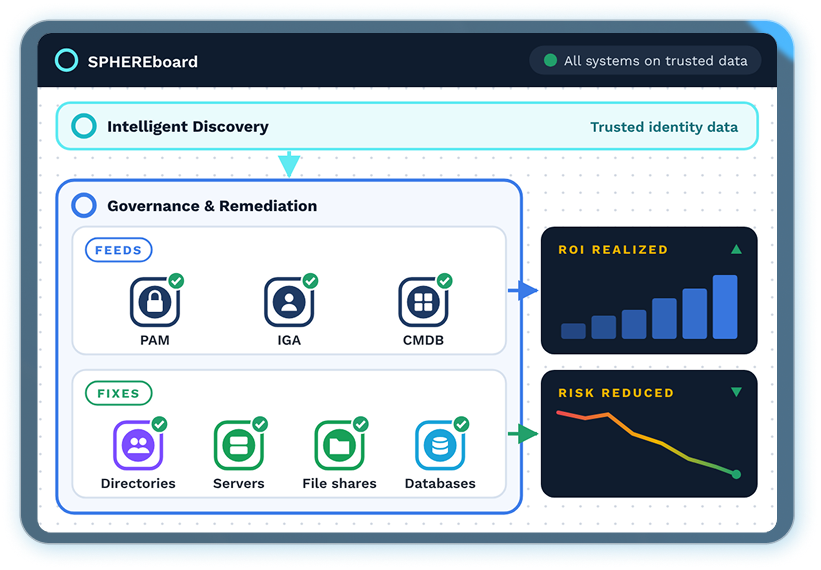
Intelligent Discovery shows you what’s there and where the risk is. Governance & Remediation acts on it: feeding accurate, owned data into CyberArk, SailPoint and ServiceNow, keeping ownership current, and fixing risky access where it lives.
Act on What You Now Know
Discovery shows you what’s there. Governance & Remediation closes the loop. SPHEREboard sends trusted, owner-confirmed identity data into the tools you already run, keeps it current as your environment changes, and drives cleanup in AD, servers, databases, applications and file shares.

Feed Your Tools
Give PAM, IGA and CMDB the accurate data they need to do their jobs.

Fix at the Source
Change access where it actually lives, not just in a report.

Stay Audit-Ready
Keep ownership and access current, with evidence and progress you can show.
The Challenge Isn’t Just Finding Problems, It’s Fixing Them
Tools Running on Bad Data
CyberArk, SailPoint and ServiceNow are only as good as the data they’re given. Onboarding, certifications and change records stall on incomplete or unowned accounts.
No One to Sign Off
Without a confirmed owner, every cleanup turns into an investigation, and risky access stays because no one will approve removing it.
Fear of Breaking Production
Changing an AD group or a file share permission without knowing what depends on it risks an outage, so nothing gets changed.
From Trusted Context to Closed-Loop Remediation
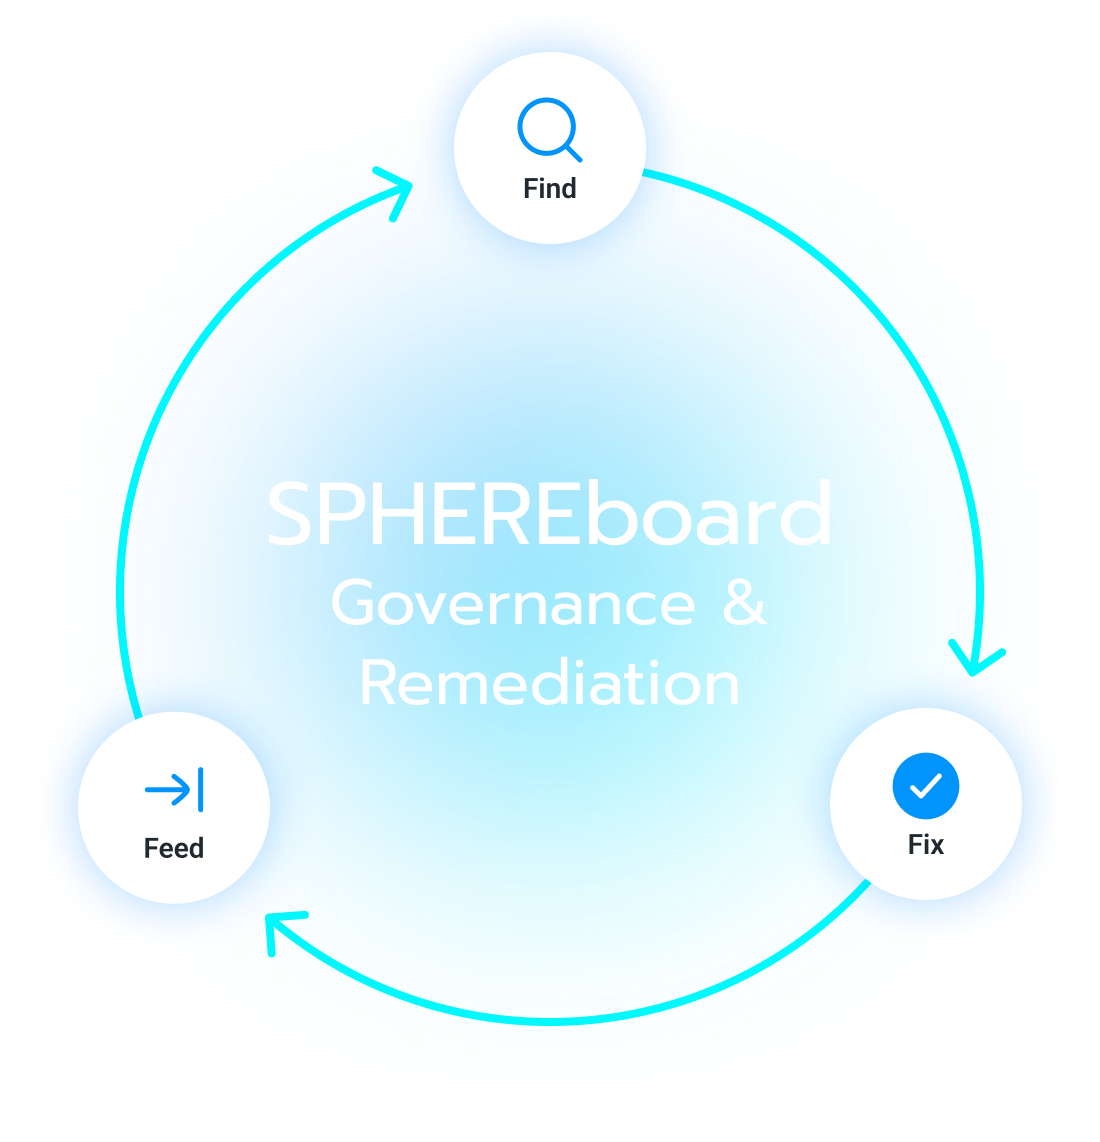
Industry analysts call this emerging space Identity Visibility and Intelligence Platforms (IVIP): connecting identities to their owners and access, revealing the relationships between them, and applying context to prioritize risk. Governance & Remediation closes the loop: it fixes issues in the same systems the data came from and feeds trusted data back to the tools that depend on it.
Governance You Can Act On
Feed Trusted Data to Your Identity Tools
PAM
IGA
CMDB
Send verified, owner-assigned accounts and business context into CyberArk, SailPoint, ServiceNow, and broader stack, so privileged onboarding, certifications and change records run on data you can trust.
Keep Ownership Current
OWNERS
CONFIRMATION
ACCOUNTABILITY
Route accounts, groups and file shares to their owners for confirmation, even figuring out the owner of the most orphaned assets, so accountability doesn’t fade after discovery.
Remediate at the Source
DIRECTORIES
SERVERS
FILE SHARES
Clean up access where it lives: remove stale and deeply nested AD groups, prune local access on servers, and tighten file share permissions. Blast-radius context and owner sign-off help changes land without breaking production.
Track Progress and Prove It
POLICY
DRIFT
AUDIT
Check accounts and access against your policies on a continuous basis, catch drift as it returns, and show measurable progress to auditors and leadership.

Trusted Data In. Lower Risk Out.
Intelligent Discovery shows you what’s there. Governance & Remediation puts that trusted data to work in CyberArk, SailPoint and ServiceNow, and fixes risk at the source. It doesn’t replace your identity solutions; it makes them work. Clean, governed identity data is also the foundation for adopting AI safely.