
SPHEREboard Intelligent Discovery
Trusted identity data starts with knowing what’s really there.
Agentlessly find accounts across your directories, infrastructure and cloud, connect them to owners and access, and see where the risk is. It’s the first step to identity data your people, processes and tools can rely on.
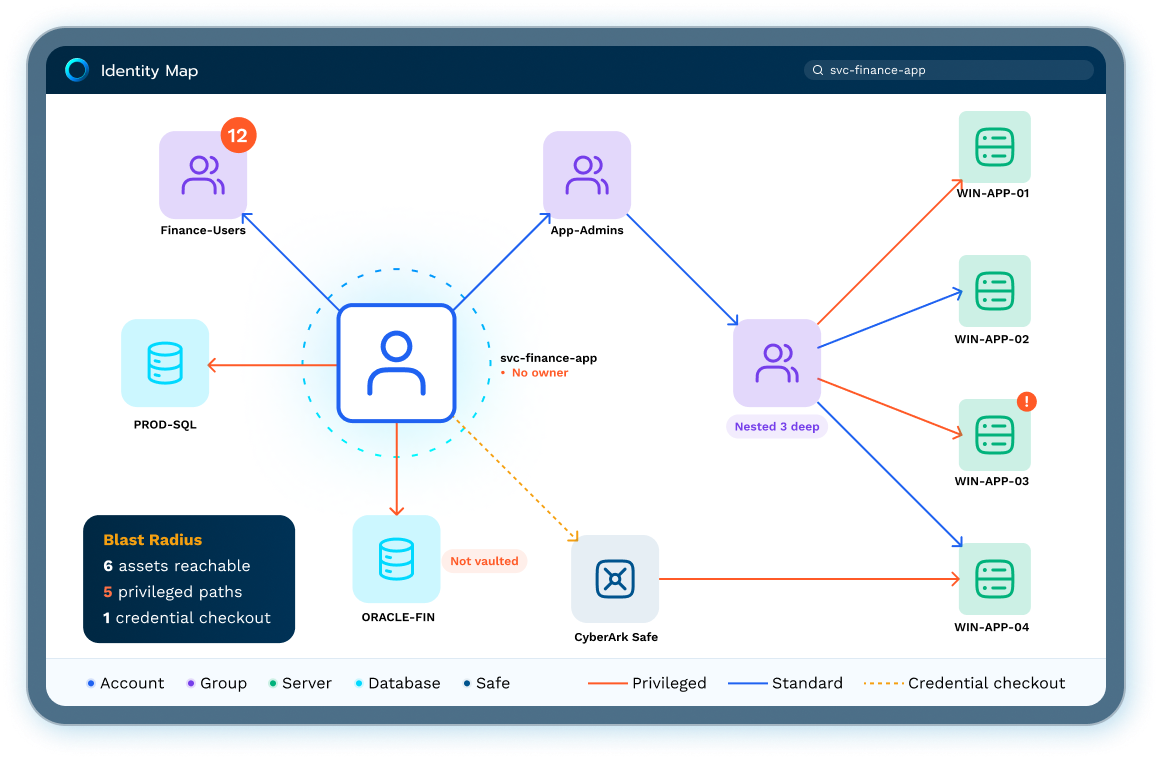
Know What’s There, and What’s Risky.
Identity data is scattered across IGA, PAM, CMDB, directories, servers and file shares, and each holds only part of the picture. SPHEREboard Intelligent Discovery agentlessly brings accounts across applications, file shares, on-prem infrastructure and cloud into one continuously updated inventory your identity program can trust.
Then see where the risk is: privileged access that isn’t vaulted, accounts with no owner, and access far beyond what anyone needs.

See Across Systems
Bring scattered account data together for a clearer picture of your environment.

Keep Visibility Current
Maintain an up-to-date inventory as accounts and systems change.

Spot Risk First
Surface the riskiest accounts and access before an auditor or attacker does.
The Challenge Isn’t a Lack of Identity Tools — It’s a Lack of Trusted Identity Data
Most organizations don’t lack identity tools — they’ve already invested in IGA, PAM, and CMDB. The real problem is that identity data is scattered across disconnected systems, each holding only part of the picture, with no connected view across all of them.

Fragmented, Manual Processes
Identity data is scattered across systems that don’t talk to each other — often stitched together with unvetted scripts and outdated spreadsheets.

Limited Observability
Privileged access sprawls unseen, and accounts stay active for years with no owner, until an alert fires and nobody can say what they can reach.

Data Nobody Trusts
Every tool shows a different version of the truth. When nobody trusts the data, responding to audits effectively becomes very hard.
From Fragmented Data to Trusted Context
Industry analysts call this emerging space Identity Visibility and Intelligence Platforms (IVIP): connecting identities to their owners and access, revealing the relationships between them, and applying context to prioritize risk. Intelligent Discovery is where building that foundation begins.
Visibility You Can Trust
Discover Every Account, Everywhere
DIRECTORIES
INFRASTRUCTURE
CLOUD
PAM / IGA
Continuously and agentlessly collect accounts and permissions from AD and Entra, Windows, Unix, databases, applications, file shares, AWS and Azure, plus what your PAM, IGA and CMDB tools already know.
Identify the Real Owner, Automatically
VERIFIED OWNERS
ACCOUNTABILITY
FASTER REVIEWS
Assign human owners and resolve orphaned assets, closing the accountability gap that stalls governance and audits.
Map Relationships and Dependencies
IDENTITIES
ACCOUNTS
SYSTEMS
Understand how identities, access, and systems actually relate — so when an alert fires, you see the full blast radius instantly instead of guessing.
Enrich With Business and Risk Context
BUSINESS CONTEXT
RISK
PRIORITIZATION
See identity data through a business lens: production vs. development, Tier 0 and Tier 1 assets, and systems in regulatory scope. Then layer in risk, such as unvaulted privileged accounts, dormant accounts and excessive access, to prioritize what matters most to the business.
Find It. Own It. See the Risk.
What Intelligent Discovery revealed for three enterprises.
Find
~17x
more privileged identities than the team knew existed
Global manufacturer
Own
20% → 90%
non-human accounts catalogued with a confirmed owner, before vs. after
National Airliner
See the Risk
93%
of assets reachable from a single account
Global financial services

Start With a Foundation You Can Trust. Then Fix What You Find.
Intelligent Discovery makes identity data complete, trustworthy and actionable. When you’re ready, Governance & Remediation puts it to work: feeding trusted data into CyberArk, SailPoint and ServiceNow, and cleaning up access at the source. Trusted identity data is also the foundation for adopting AI safely.